Your security manager reviews the risk register on Monday. Wednesday brings a revision to a cloud access policy by a developer. The week ends with a new security procedure on file while the Statement of Applicability has not been updated beyond the older version.
At first glance, none of these changes seems particularly alarming. When an ISO 27001 auditor reviews the records, even small inconsistencies can become difficult to explain. For startups, the challenge is often managing compliance tasks while the team is busy running the business.
Why Manual Compliance Tracking Takes So Much Time
For many teams, spreadsheets offer a simple and inexpensive way to organize information. However, spreadsheets can fall out of date without anyone noticing. A growing business may begin with separate trackers for risks and control responsibilities. That arrangement can work while the project has few moving parts, but problems appear when responsibilities shift or several employees make independent updates.
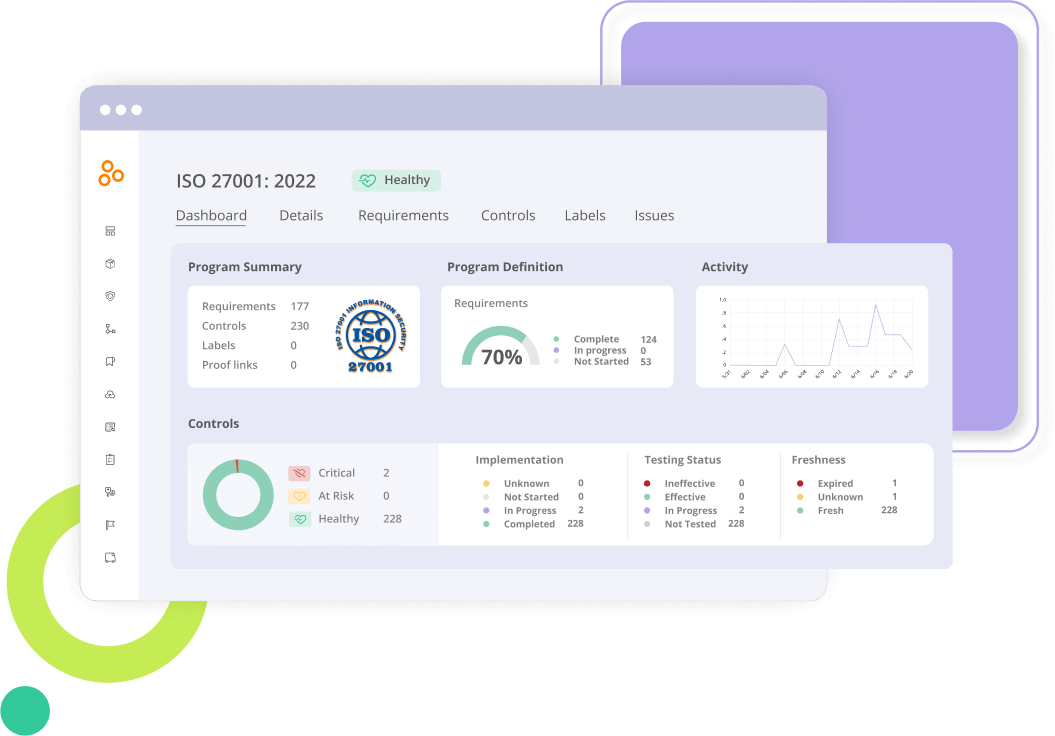
ISO 27001 compliance software offers an alternative by bringing related activities into a structured workspace. A shared workspace makes it easier to review control documentation and status together in one place.
Before You Subscribe, Identify Who Will Keep It Updated
Before purchasing another subscription, ask a important question: Who will actually maintain this system?
The compliance needs of an eight-person startup are not necessarily comparable to those of a multinational business. Responsibility may be shared: founders oversee risk decisions, developers manage technical controls, and operations staff coordinate records.
A useful ISO 27001 software platform supports clear assignments without unnecessary complexity. If employees are reluctant to update a system, its capabilities are unlikely to deliver much practical benefit.
The Statement of Applicability Needs Accurate Records
The Statement of Applicability serves a purpose beyond meeting an administrative requirement. The document records which controls are considered necessary, the reasons for those decisions, and their implementation status.
Using cloud infrastructure does not remove the need to consider applicable physical security responsibilities, even when the provider manages the underlying buildings.
Clear documentation should explain the reasoning behind its control choices. Linking the risk register with the Statement of Applicability helps an auditor understand why controls were chosen.
What Happens When the Auditor Arrives?
An auditor may ask to examine records of access management, employee training evidence, security policies, or risk treatment decisions. Finding the latest approved documents becomes unnecessarily slow when records are spread across several systems. ISO 27001 certification software helps organize these materials, but it does not guarantee that the evidence is sufficient or that certification will be granted.
An accredited certification body, not the software provider, determines the outcome of its certification assessment. Keeping records clear and accessible helps the team manage the assessment more efficiently.
A More Manageable Approach for Startups
A growing team should compare compliance platforms against its financial and operational constraints. For teams researching the best compliance software for startups ISO 27001 certification, CertAssist provides a practical approach. The platform includes ISO 27001 clauses, Annex A controls, a risk register, a Statement of Applicability, editable policy guidance, and evidence storage.
CertAssist also allows direct auditor access without requiring the business to integrate its infrastructure. This approach may suit organizations that want to maintain their own records.
Make ISO 27001 Preparation Easier to Manage
Certification preparation should not prevent employees from focusing on customers, product development, and daily operations. A manageable system supports up-to-date evidence, visibility into incomplete work, and preparation for an independent audit.
CertAssist aims to give smaller businesses a practical framework for compliance tasks without excessive administrative complexity. The number of available features does not necessarily tell you whether a team will maintain it. What matters is whether your team can keep its security responsibilities organized as the business grows.